




Latest from X
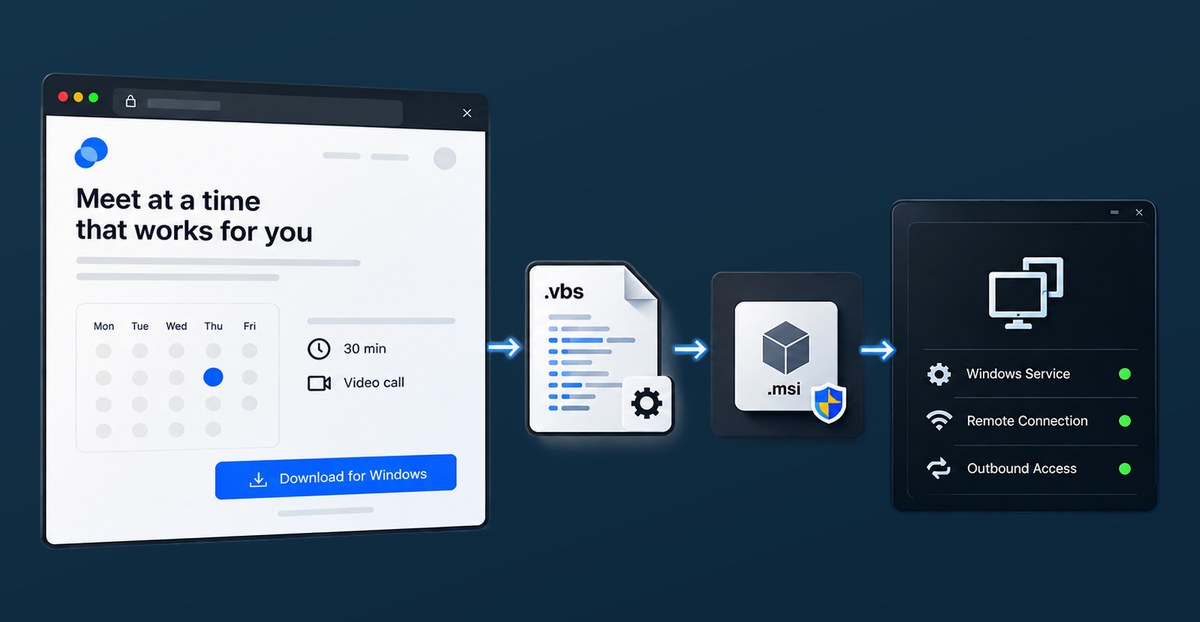
- Two new samples from a single Hunting query — a ScreenConnect downloader and a PowerShell backdoor
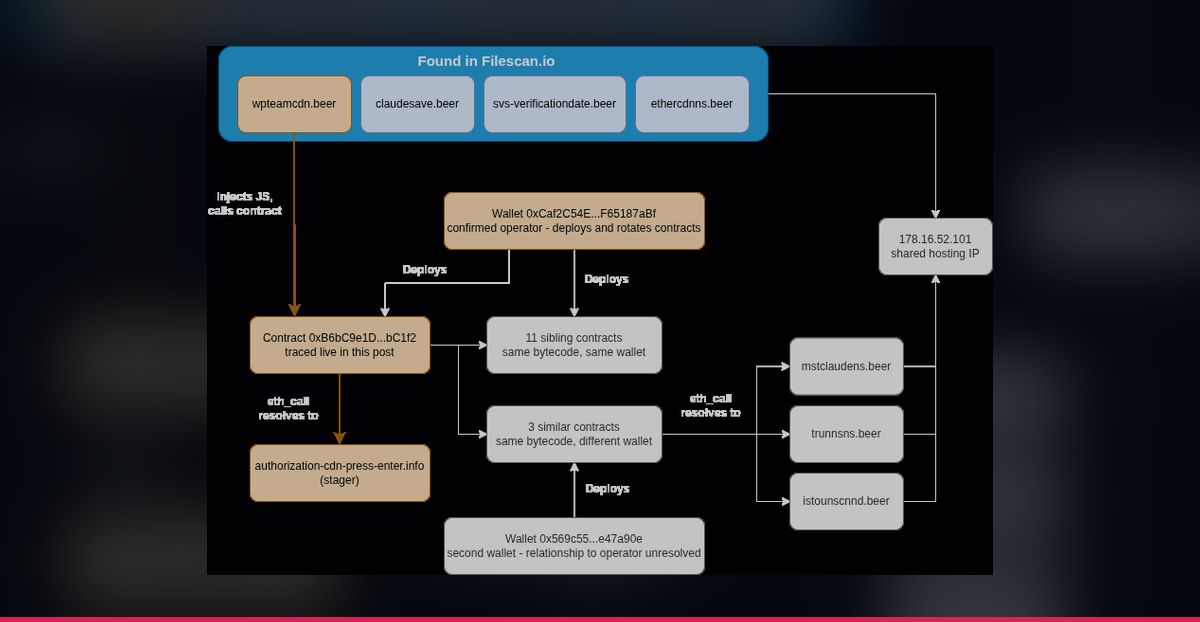
- Tracing a live ClickFix chain via EtherHiding — lure page to Polygon contract to stager domain
- ShinyHunters PeopleSoft — two unreported Go dropper variants share one MeshCentral C2 via azurenetfiles[.]net
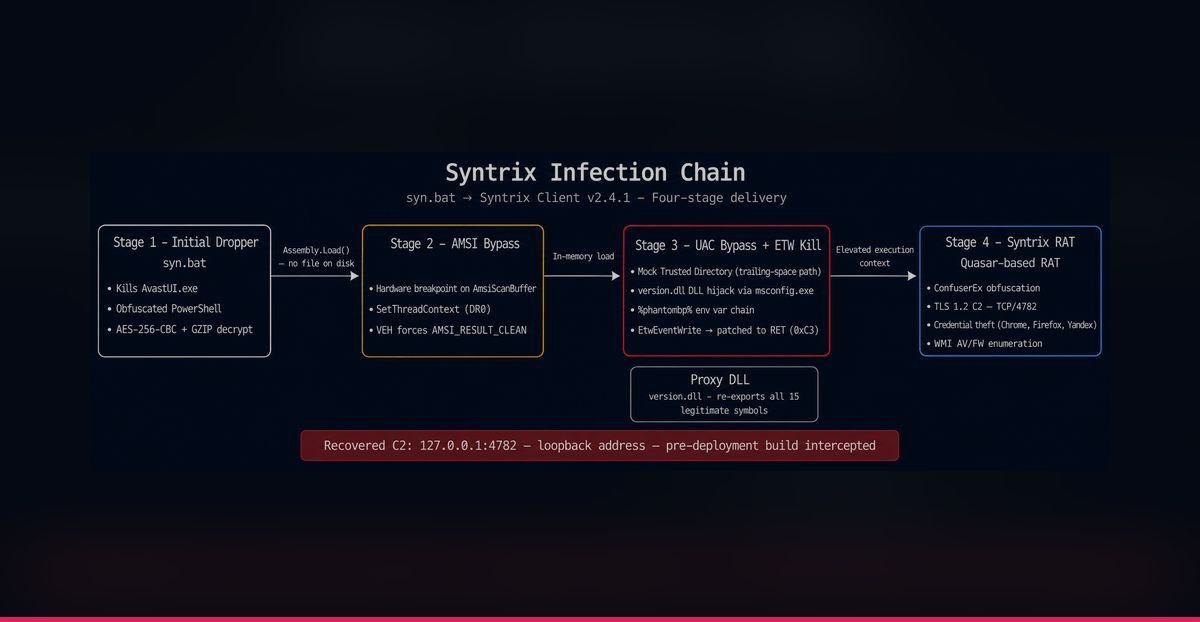
- Syntrix RAT caught pre-deployment — four-stage chain, AMSI and UAC bypass, ETW patching, C2 still on 127.0.0.1:4782
- ClickFix did not die with 2025 — fake Cloudflare CAPTCHA hijacks the clipboard to drop a malicious OCX